Background
This case study covers two pieces of real work. First, we rebuilt a client's two WordPress sites, an English site and a Japanese site for a professional-services business, as one bilingual Next.js (React) application with its own React-based CMS. It launched in October 2026 and the old WordPress server was retired. Second, we hardened the contact forms on our own website, itsupportintokyo.com, against automated submissions. Together they form the security pattern we now offer to WordPress migration clients. The client is anonymised, and we leave out details that could help an attacker.
Challenge
The client ran a separate WordPress installation for each language, with a stack of plugins for SEO, security, forms and marketing. Every plugin, theme and PHP update was one more thing to maintain, and editing two language versions in two admin screens was slow. The old site's login-protection plugin had recorded more than 500 lockouts of repeated failed sign-in attempts across the two installations, a reminder that a public WordPress login page is a constant target. More generally, a public form that sends email attracts automated spam, and a form that lets the browser write straight into a database can be abused. Shared admin passwords and admin areas without two-factor sign-in are common weak points on small-business sites. The goal was to keep every useful URL and the site's search visibility, give staff an editor that felt familiar, and remove these risks.
What We Did
Inventory URLs and content before writing code
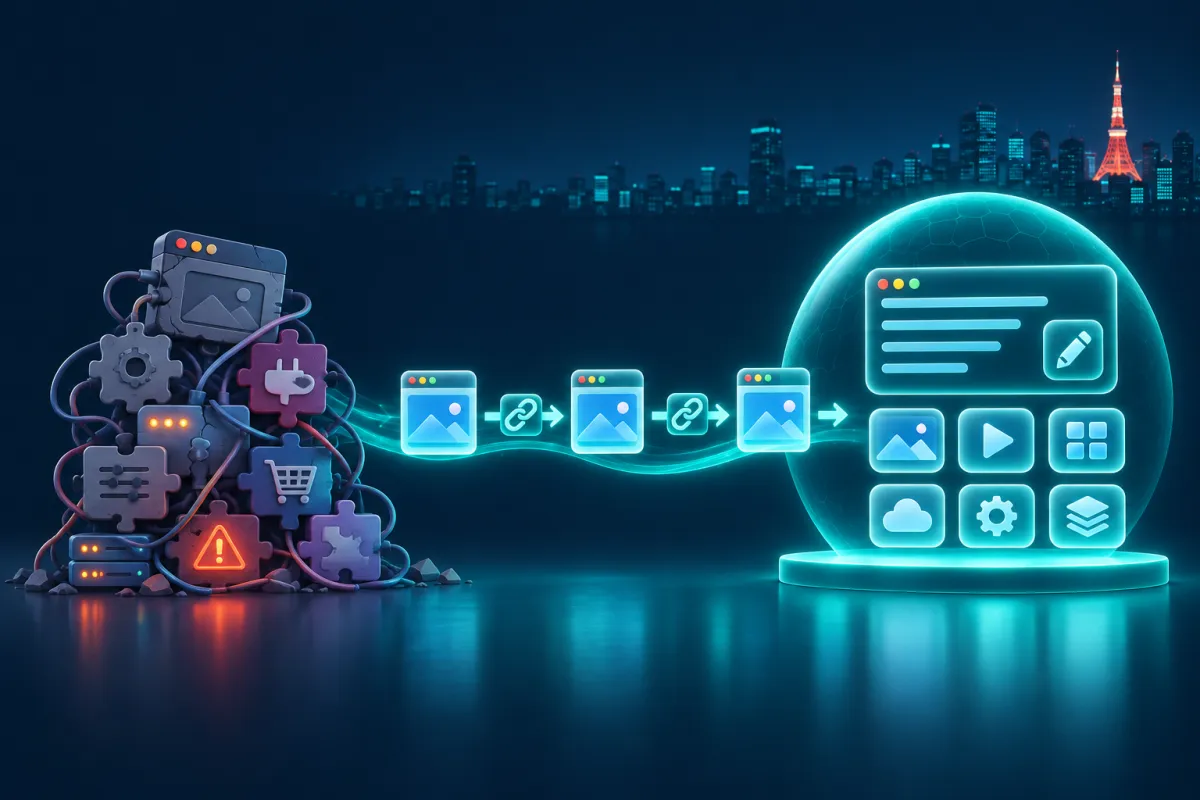
We exported both WordPress sites and wrote migration scripts that read posts, pages, media and SEO fields from the WordPress database. 76 permanent (308) redirect rules send old WordPress addresses, including /index.php/ paths, the separate Japanese-language section and /wp-content/uploads/ media links, to their new pages, and automated tests check them.
One bilingual Next.js site with a React-based CMS
English and Japanese now live in one Next.js application. Staff sign in to a bilingual admin modelled on what they knew from WordPress, Polylang and Yoast: posts, pages, media, menus, redirects, revisions and SEO fields. Content is stored in a Supabase database in Tokyo, and HTML is sanitised both when it is saved and when it is shown.
Two-factor sign-in and roles for the CMS
Admin accounts must use an authenticator app (TOTP 2FA). 2FA secrets are stored encrypted, one-time recovery codes are stored hashed, and repeated wrong codes trigger a lock that grows longer each time. Each person has their own account with an admin, editor or author role, can see signed-in devices and sign them out remotely, and setting a new password signs the account out everywhere else.
A locked-down back end and modern browser protections
The database uses row-level security with no public access, so only the server can read or write content. The site sends a per-request Content Security Policy and standard security headers, checks uploads by their actual file contents, logs admin activity, and runs automatic weekly backups.
Layered bot protection on contact forms (our own site)
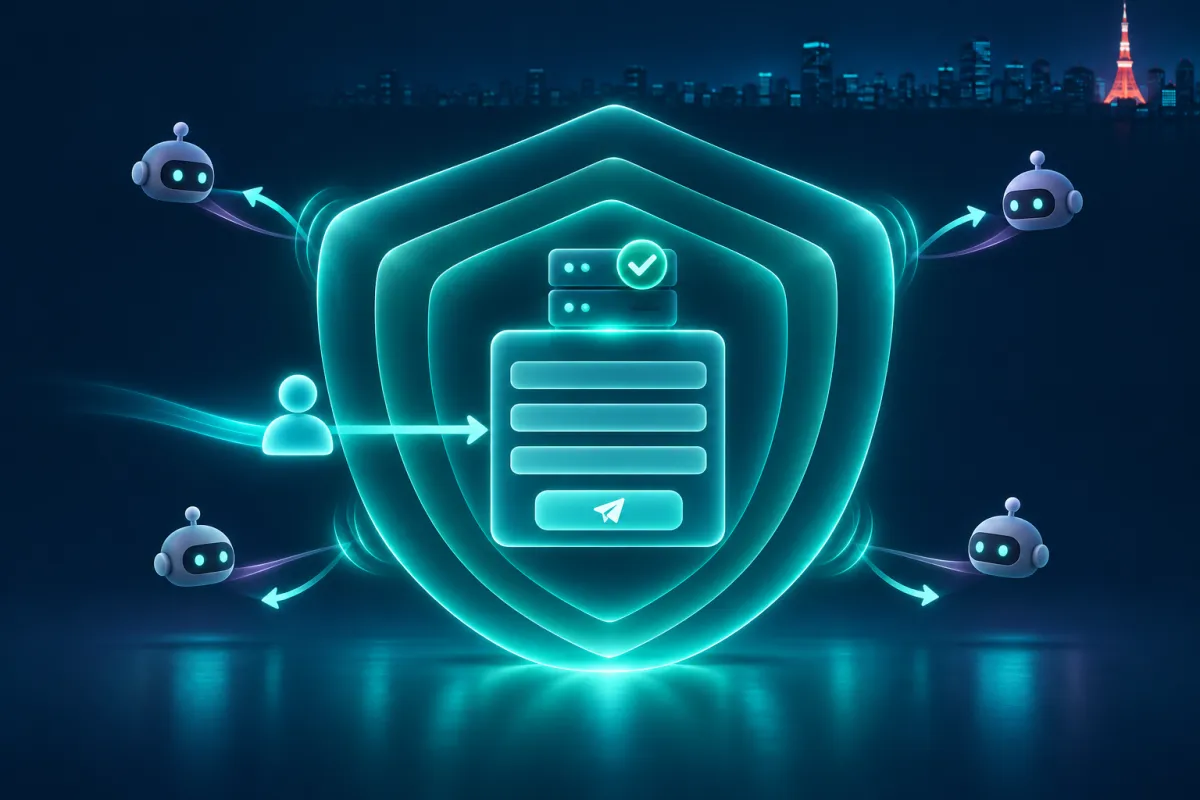
On itsupportintokyo.com, contact submissions are checked with Cloudflare Turnstile, verified on the server (token, hostname and action), and also go through a hidden honeypot field, an allowed-origin check, length and format validation, and a rate limit per email address and per hashed IP. Submissions go through a server function, so browsers cannot write to the enquiry table directly. Security data such as IP addresses is anonymised after 90 days, and enquiries are deleted after 180 days.
Results
- The new bilingual site launched in October 2026 and replaced WordPress. The old WordPress server and its static IP address were retired
- The public site no longer runs PHP or plugins and has no WordPress login page to attack
- Old WordPress URLs are handled by 76 tested permanent redirects, so existing links and bookmarks still lead to the right pages
- Every admin signs in with 2FA, and staff edit both languages in one React-based CMS
- The client's enquiry form is the third-party form service they already used, embedded on the new site, so no enquiry data passes through it
- On our own site, the layered checks are designed to stop automated contact-form submissions before they reach our inbox or database
What This Means for You
Moving off WordPress is more than a redesign. Done carefully, it lets you keep your search visibility, give staff a simpler editor, and close the most common ways in at the same time: exposed login pages, outdated plugins, shared passwords and unprotected forms. An SEO-safe URL map, a React-based CMS with 2FA and roles, a locked-down database and bot-resistant forms: that is the setup we offer WordPress migration clients. If your site runs on WordPress and you want the same, book a free consultation.