Nitori Data Breach: Up to 37.62 Million Customer Records May Have Leaked (Nov 2026)
Key takeaways
Nitori says up to 37.62 million records (names, addresses, phones, birth dates) may have leaked; passwords and cards were not. What Nitori said, what is unknown, and what to do.
Nitori Holdings, Japan's largest furniture and homewares retailer, said on Nov 9, 2026 that up to 37.62 million records of personal information may have leaked after a third party got into a system it manages. Nitori found the intrusion on Friday, Nov 6, blocked it the same day, and has since found signs of access as early as mid-to-late October. Names, email addresses, home addresses, phone numbers, dates of birth and gender are in scope; login passwords and credit card details are not, Nitori says. Here is what Nitori itself has said, what is still unknown, and what customers and businesses in Japan should do now.
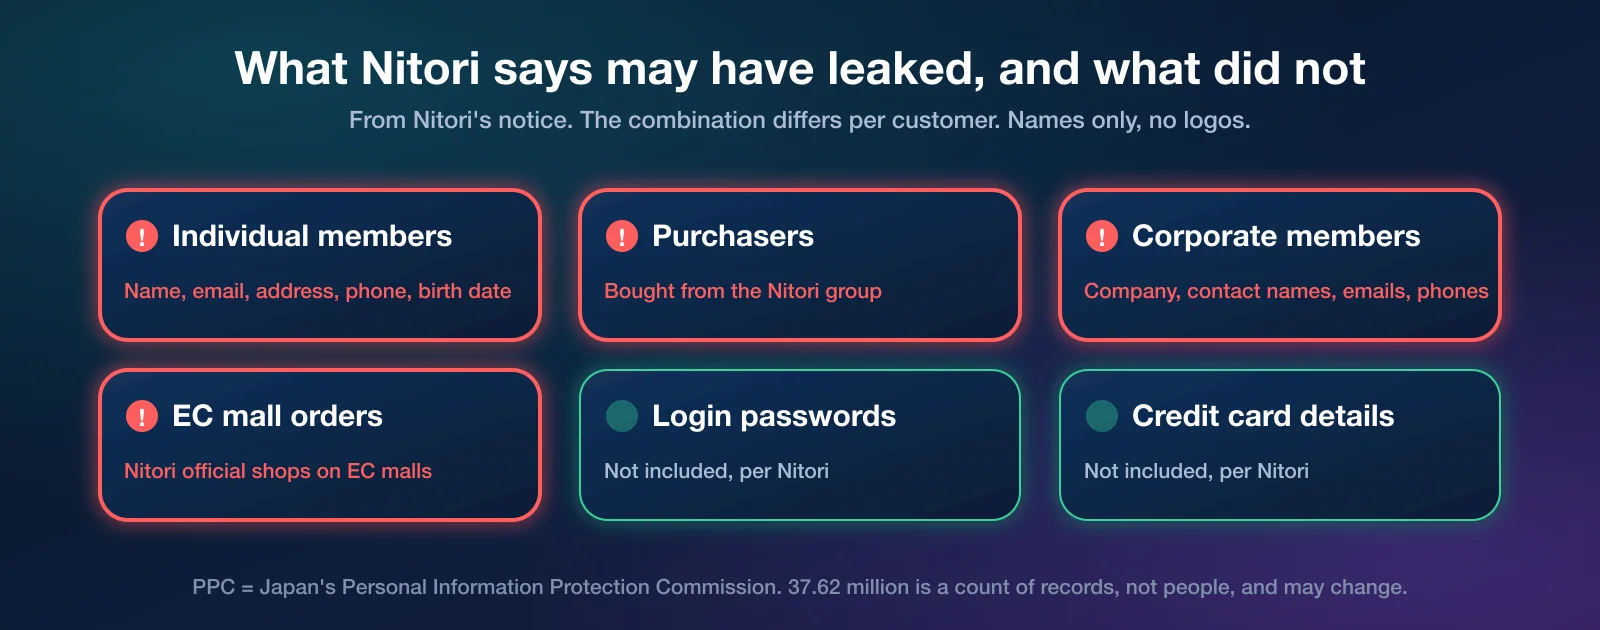
- Who: Nitori Holdings Co., Ltd. (ニトリホールディングス), covering Nitori group individual members, purchasers, corporate members, and orders placed through Nitori's official shops on e-commerce malls.
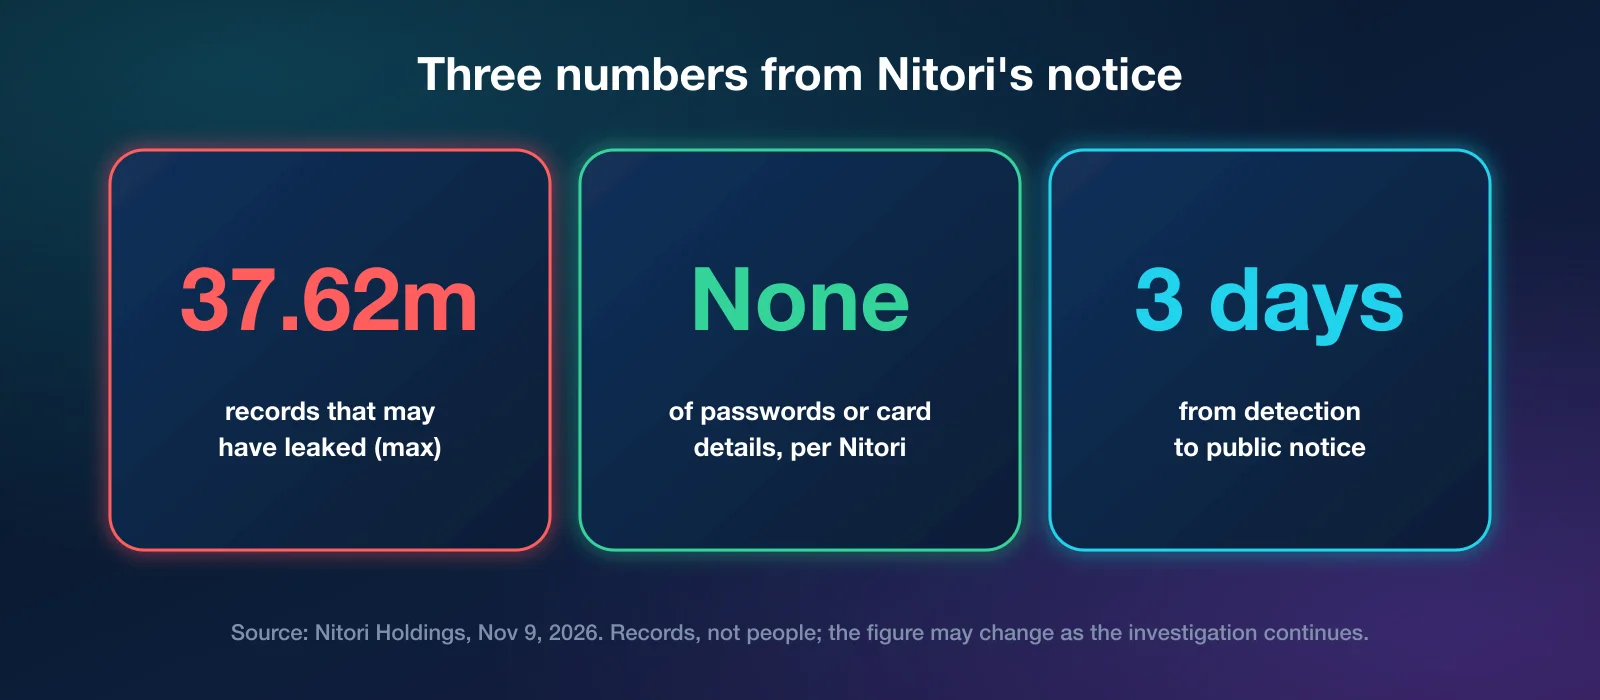
- Scale: up to 37.62 million records may have been taken. This is a count of records, not people, and Nitori says it may change.
- Not included: login passwords and credit card information, per Nitori.
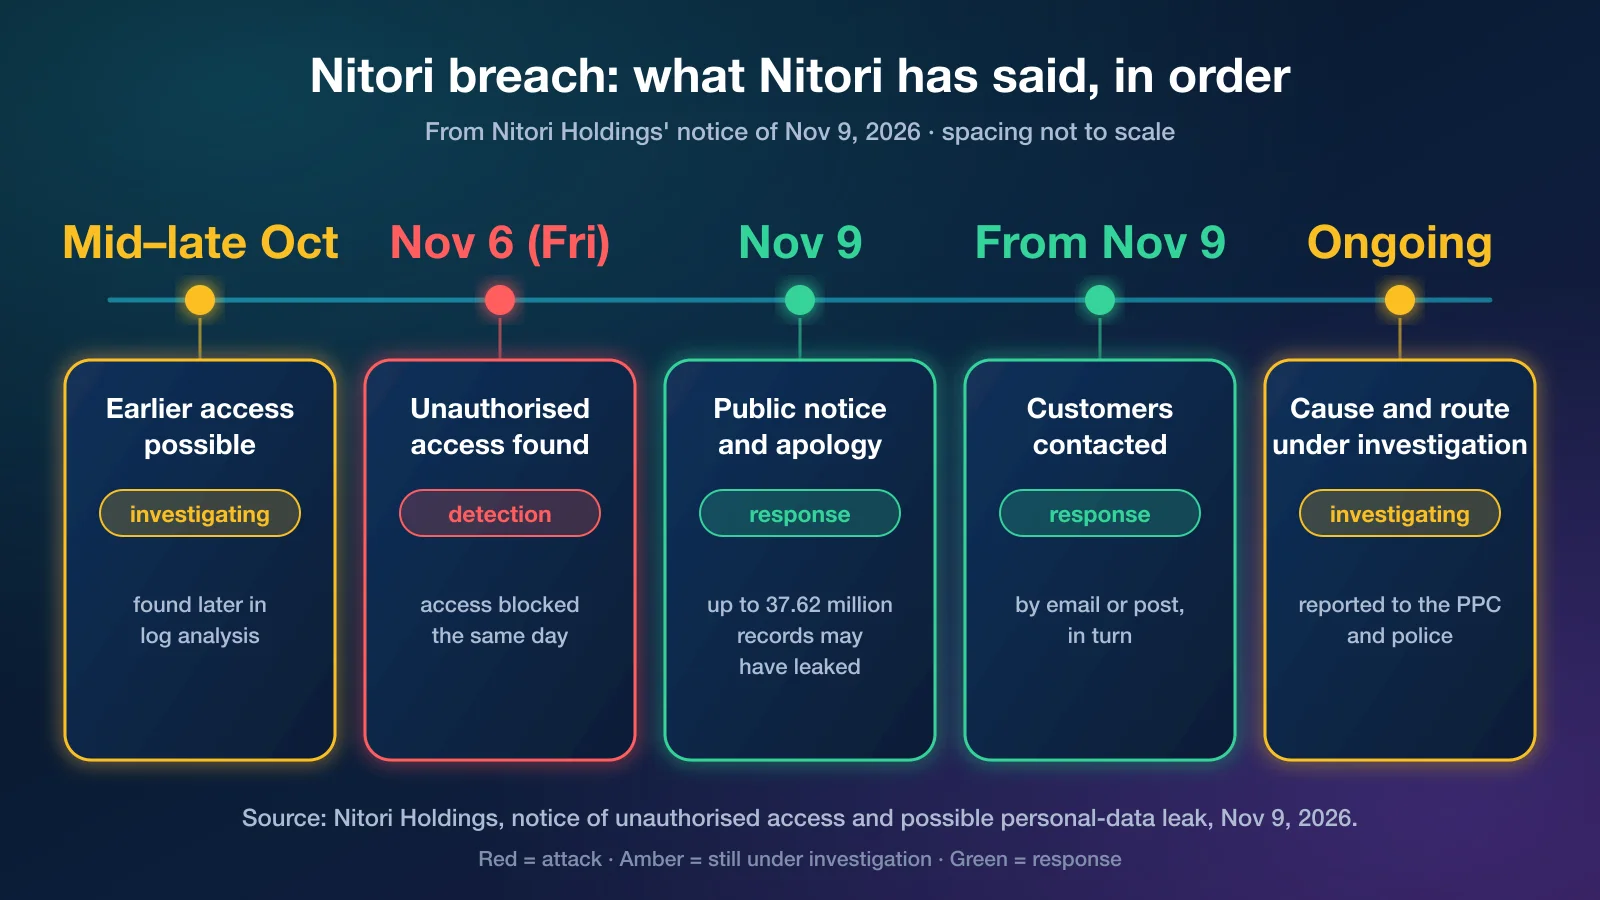
- Timeline: possible access from mid-to-late October; intrusion found and blocked on Nov 6; public notice on Nov 9; affected customers contacted by email or post, in turn.
- Still unknown: how the attacker got in, who it was, and whether data has been misused. Nitori has reported the case to Japan's Personal Information Protection Commission and the police.
What Nitori has said
Nitori published a three-page notice and apology on its corporate news page on Nov 9 (PDF, Japanese; also listed on nitorihd.co.jp/news and the Nitori Net notice page). In summary:
- Nov 6 (Fri): Nitori confirmed unauthorised access by a third party to a system it manages, blocked the access immediately, and began an investigation with outside specialists.
- Mid-to-late October: log analysis after Nov 6 showed that a third party may have accessed the system before that date too. Nitori says the details are still under investigation.
- Nov 9: public notice. Up to 37.62 million records of personal information held on its servers may have been taken. Nitori says it has fixed the vulnerable point, strengthened monitoring, and continues to block the attacker.
- From Nov 9: affected customers will be contacted by email or post, in turn.
- Authorities: Nitori is reporting to and consulting with the Personal Information Protection Commission (個人情報保護委員会) and the police.
What may have leaked, and what did not
Nitori lists four groups of data. The combination differs for each customer.
- Individual members and anyone who bought from the Nitori group: member number, name (with furigana reading), email address, home address, phone number, date of birth, gender.
- Corporate members: member number, company name, department, representative's name, company address and phone number, and the contact person's name, email address and phone number.
- Orders: order data for Nitori products bought through Nitori Net and Nitori's official shops on e-commerce malls.
- Not included: credit card information and login passwords.
Two points are easy to get wrong. First, 37.62 million is a count of records, not of people: one person can appear as a member and as a purchaser, and a business can appear as a corporate member and in orders. Second, it is a maximum. Nitori says the number may change as it finishes log analysis and data matching.
What has not been said yet
Nitori's notice does not say how the attacker got in, which system was involved beyond "a system the company manages", whether a ransom was demanded, or whether any group has claimed the attack. It also does not say the data has appeared anywhere online. Japanese coverage from NHK and Nikkei reports the same facts as the notice. We will update this story if Nitori publishes a follow-up report.
Part of a run of Japanese retail breaches
Nitori's notice came days after another large one. On Nov 5, Iris Plaza, the Iris Ohyama group company that runs the Iris Ohyama online store, said in its second report that data on about 7.7 million people stored in an external cloud service may have been viewed or taken: about 5.8 million members (including former members, with encrypted passwords) and about 1.9 million non-members. It found a suspicious file on Oct 28, stopped the site, and reported to the police and the Personal Information Protection Commission on Oct 29; card details were not stored there, it says. The two cases are unrelated as far as either company has said. Together with the GMO Desktop Cloud breach, they make this autumn one of the busiest on record for disclosed incidents in Japan.
If you have shopped at Nitori
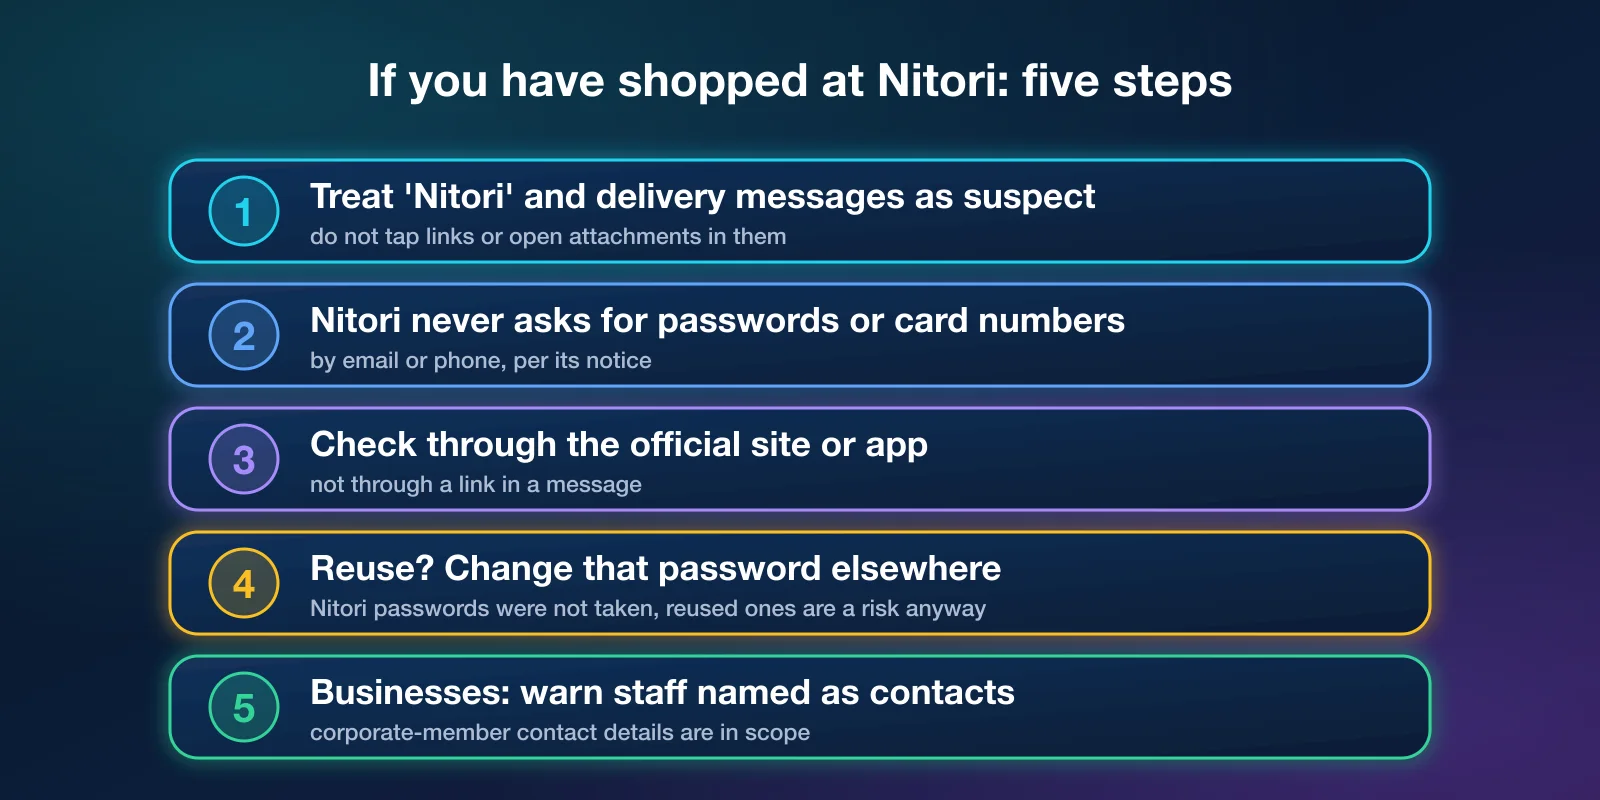
- Treat messages that mention Nitori, a delivery or an online mall as suspect. Nitori warns that the leaked data may be used for impersonation emails, phishing and suspicious phone calls. With your real name, address and phone number, a fake "delivery problem" or "refund" message can look very convincing. Do not tap links or open attachments in them.
- Nitori will not ask for your password, card number or PIN by email or phone, its notice says. Anyone who does is not Nitori.
- Check through the official site or app, never through a link in a message. If you are unsure about a message, use the contact details on Nitori's official site rather than the ones in the message.
- Change any password you reused. Nitori says login passwords were not taken. But if your Nitori password is the same as one you use elsewhere, now is a good time to change it there and turn on two-step verification.
- Businesses: warn the staff you registered as contacts. Corporate-member data includes the contact person's name, email and phone, which makes targeted business-email scams easier. A short note to those staff, and to accounts payable, costs nothing.
Want a phishing-ready check of your company's email and accounts?
We help Tokyo businesses turn on two-step verification, set up email authentication (SPF, DKIM, DMARC) and brief staff on fake delivery and invoice messages, in English and Japanese. Book a free consultation.
Sources
Nitori Holdings, "Notice and apology regarding a possible leak of personal information due to unauthorised access to our system" (Japanese), Nov 9, 2026, listed at nitorihd.co.jp/news and on the Nitori Net notice page; NHK, report of Nov 9, 2026; Nikkei, report of Nov 9, 2026; Iris Ohyama / Iris Plaza, second report on unauthorised access (Japanese), Nov 5, 2026. Graphics are our own and use names only. The photo-style image was generated with ChatGPT and is not a photograph of any customer or Nitori store. IT Support in Tokyo is not affiliated with Nitori Holdings or Iris Ohyama. Nitori is a trademark of Nitori Holdings Co., Ltd.
Related: More tech news · GMO Desktop Cloud breach · IT support in Tokyo