How to Secure AI Tokens and API Keys: Lessons From the McDonald’s Chatbot Incident
Key takeaways
AI security often fails before the model runs. Learn how to protect AI API keys, tokens, admin access, server-side proxies, rotation, monitoring, and vendor integrations.
AI security does not start with the model. It starts with the keys. If an AI token, API key, admin password, webhook secret, service account, or database credential is exposed, even a strong AI system can become a data leak, cost spike, or compliance problem.
The public lesson from the McDonald’s hiring chatbot incident is not simply “AI is risky.” The sharper lesson is that AI projects often connect sensitive workflows to normal web systems: admin dashboards, applicant records, vendor APIs, databases, and support tools. If the basics are weak, the AI layer makes the blast radius bigger.
What Happened in the McDonald’s Chatbot Incident?
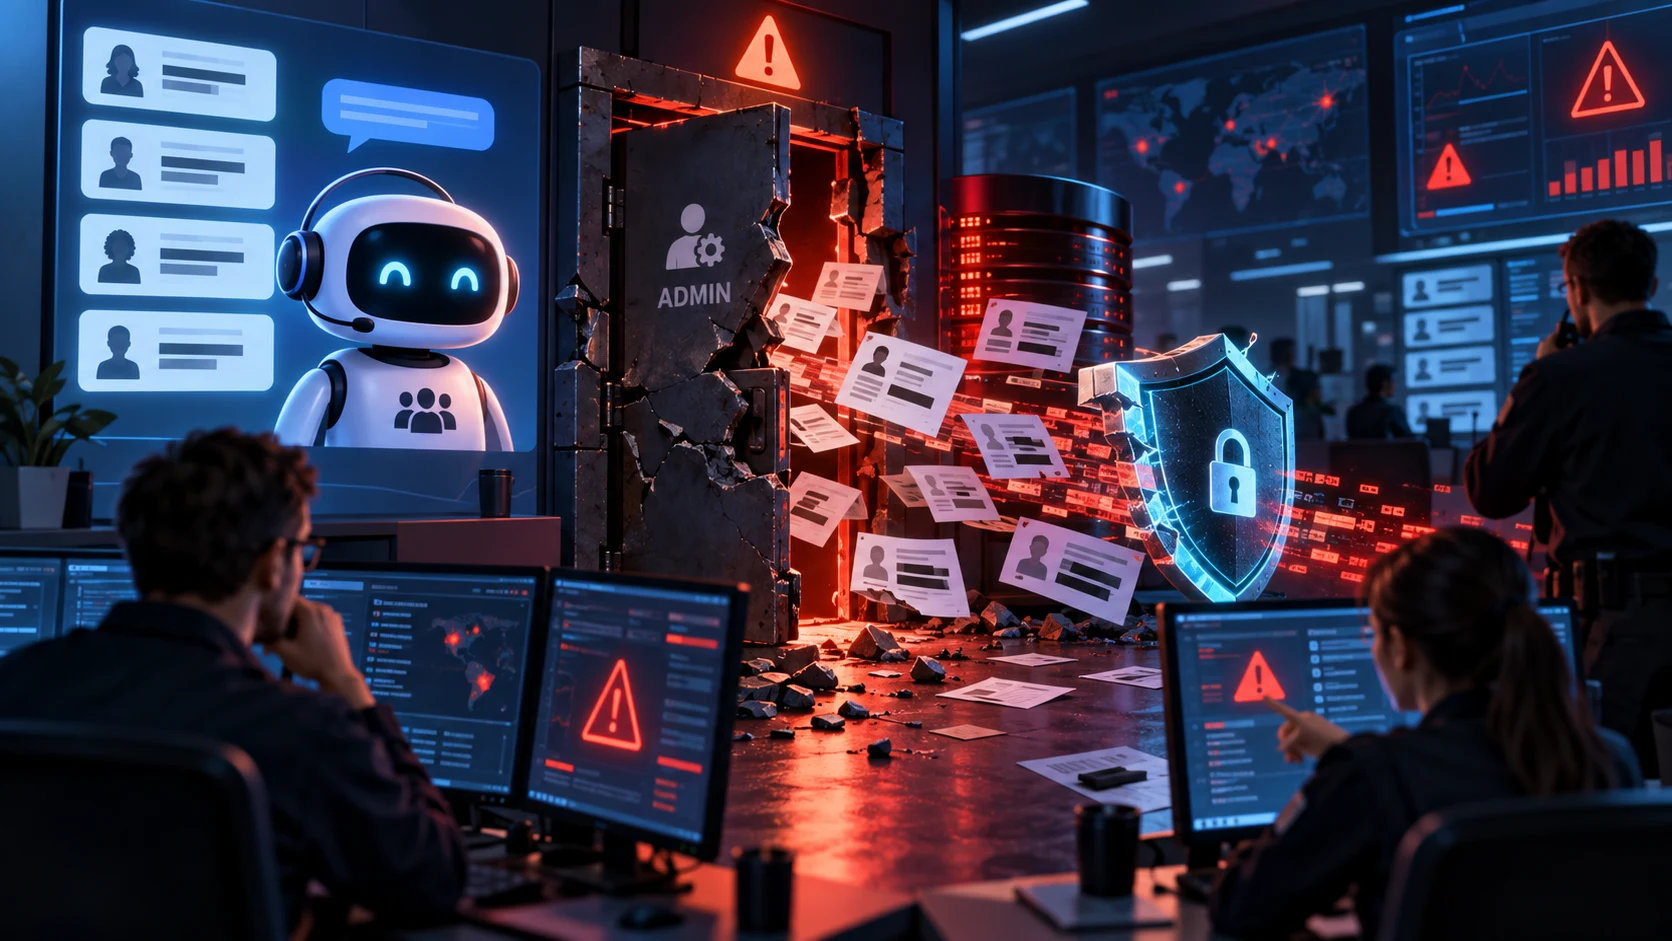
In 2025, WIRED reported that researchers found weaknesses in a McDonald’s hiring chatbot system connected to Paradox.ai. The reporting described a basic admin access issue and exposure risk around applicant data. The important takeaway for businesses is simple: an AI chatbot is still software. It has logins, vendors, APIs, databases, permissions, and operational controls.
That means AI risk is not only prompt injection or hallucination. It is also weak admin portals, default credentials, over-permissioned API keys, exposed frontend secrets, missing audit logs, and tokens that never expire.
The Real Problem: Secrets Become Infrastructure
An AI API key is not just a string. It is access to models, billing, files, assistants, embeddings, logs, tools, agents, and sometimes customer data. In a modern app, one AI key may sit beside payment credentials, Supabase service roles, Stripe webhooks, Google OAuth secrets, cloud storage tokens, Slack bot tokens, GitHub tokens, and database URLs.
Once a business adds AI, these secrets become part of daily operations. Support staff may trigger AI workflows. Websites may call an AI model. Internal dashboards may summarize documents. Recruiting tools may screen messages. Sales teams may generate proposals. If the key architecture is wrong, all of that convenience becomes risk.
Common AI Token and API Key Mistakes
| Risk | Why it matters | Better approach |
|---|---|---|
| API key in frontend code | Anyone can inspect browser JavaScript and copy the key. | Call AI providers from a server-side route or edge function. |
| One shared master key | A single leak can expose every environment and workflow. | Use scoped keys by app, environment, workflow, and vendor. |
| No rotation plan | Old leaked keys can keep working silently. | Rotate keys on a schedule and immediately after staff/vendor changes. |
| No usage monitoring | Abuse may appear first as a cost spike or unusual API pattern. | Set alerts for spend, rate, geography, endpoint, and failed calls. |
| Vendor access too broad | A vendor issue can become your customer data issue. | Review vendor access, audit logs, retention, and data handling before launch. |
| Secrets in screenshots or docs | Teams often paste keys into tickets, chat, email, and manuals. | Use a secrets manager and redact credentials in documentation. |
A Secure AI Key Lifecycle
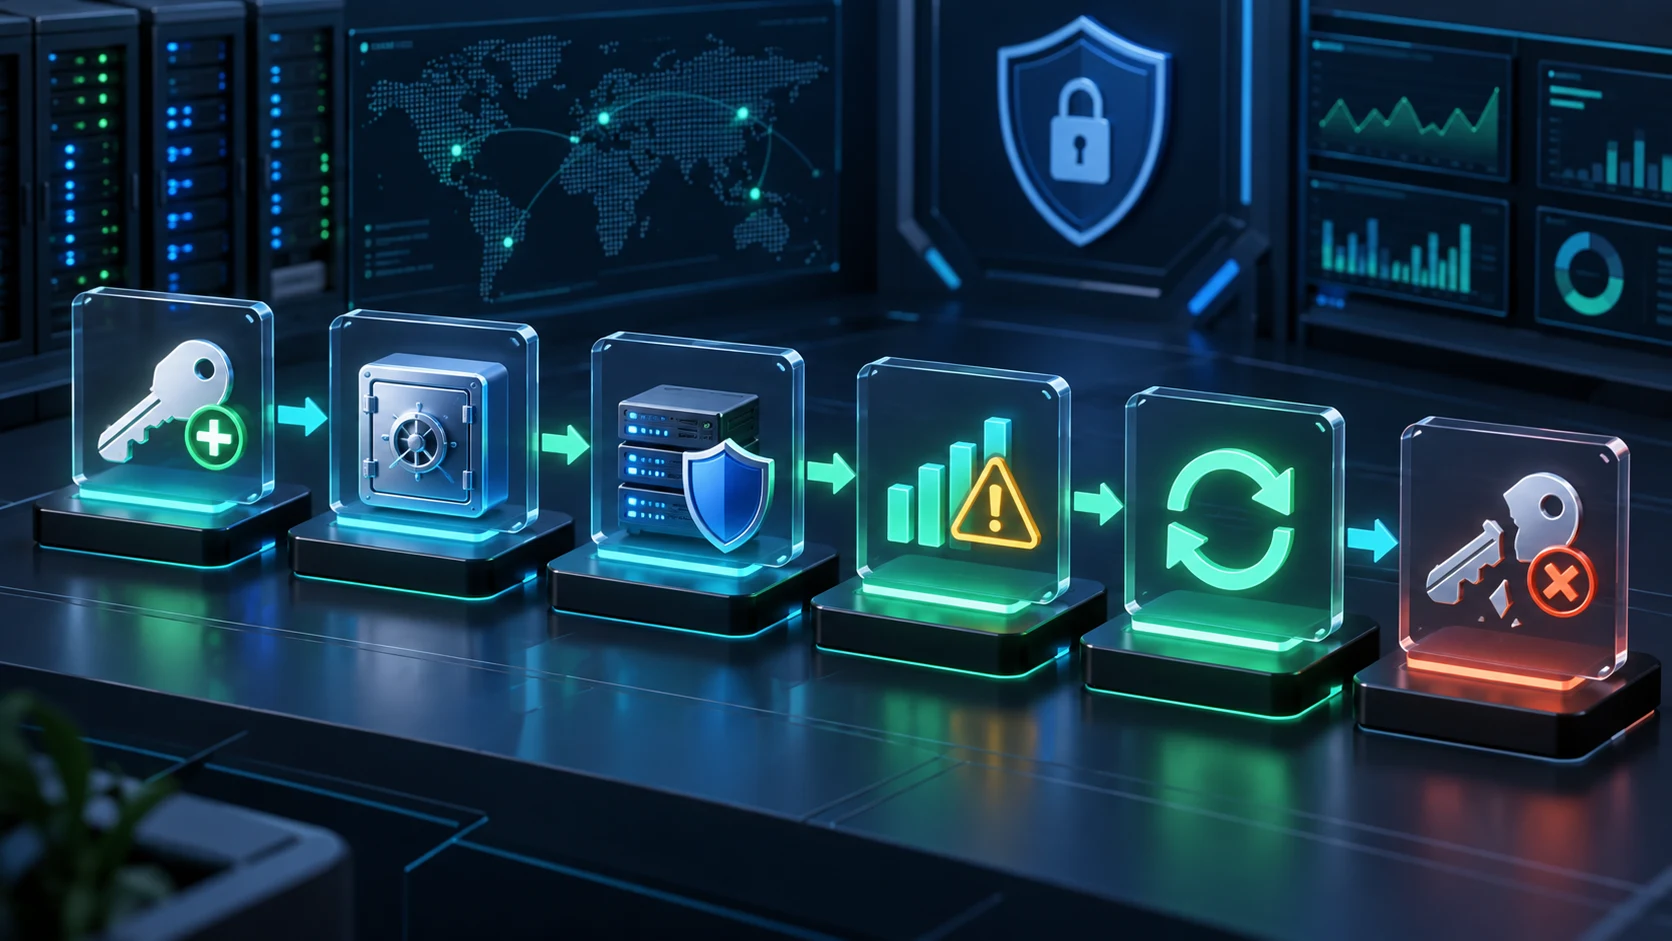
The safest AI systems treat keys like production infrastructure. Follow the lifecycle: create a scoped key, store it in a vault, call it only from trusted server code, monitor usage, rotate regularly, and revoke immediately if anything looks wrong.
Practical Checklist for Business AI Projects
- Never expose AI keys in the browser: AI provider calls should go through server-side routes, edge functions, or backend APIs.
- Use environment-specific keys: separate development, staging, and production. A test key should never access production data.
- Scope keys narrowly: one workflow should not have permission to everything.
- Store secrets in a proper vault: use platform environment variables or a secrets manager, not shared spreadsheets or chat messages.
- Rotate keys: schedule rotation and rotate immediately after suspected exposure, employee departure, vendor change, or repository leak.
- Log and monitor AI usage: watch cost, prompt volume, file access, failed requests, rate-limit errors, and unusual endpoints.
- Proxy and validate requests: validate user identity, organization, rate limits, input size, and allowed tools before the AI provider call.
- Keep sensitive data out when possible: do not send personal data, HR data, financial records, or customer secrets unless the workflow truly requires it.
- Review vendors: ask how vendors store prompts, files, logs, API keys, and admin access.
- Prepare an incident plan: know who revokes keys, disables workflows, reviews logs, notifies stakeholders, and restores service.
Why IT Support in Tokyo Wins Here
Many companies can connect an AI API. Fewer can design the security and operations around it. IT Support in Tokyo approaches AI implementation like an IT and software security project: identity, permissions, cloud architecture, data boundaries, admin dashboards, logs, monitoring, backups, and recovery.
We build secure AI workflows for the real business environment, not just demos. That means custom server-side integrations, safe admin tools, role-based access, secret rotation, usage alerts, cloud deployment, and documentation your team can actually follow.
Sources and Further Reading
- WIRED: McDonald’s AI hiring chatbot incident
- OWASP Secrets Management Cheat Sheet
- OWASP API Security: Broken Object Level Authorization
- OpenAI production best practices
- Anthropic Admin API key documentation
Need Secure AI Workflows?
IT Support in Tokyo helps companies design secure AI integrations, protect API keys, build server-side AI workflows, audit vendor access, and deploy custom business automation safely. Contact us to review your AI security plan.